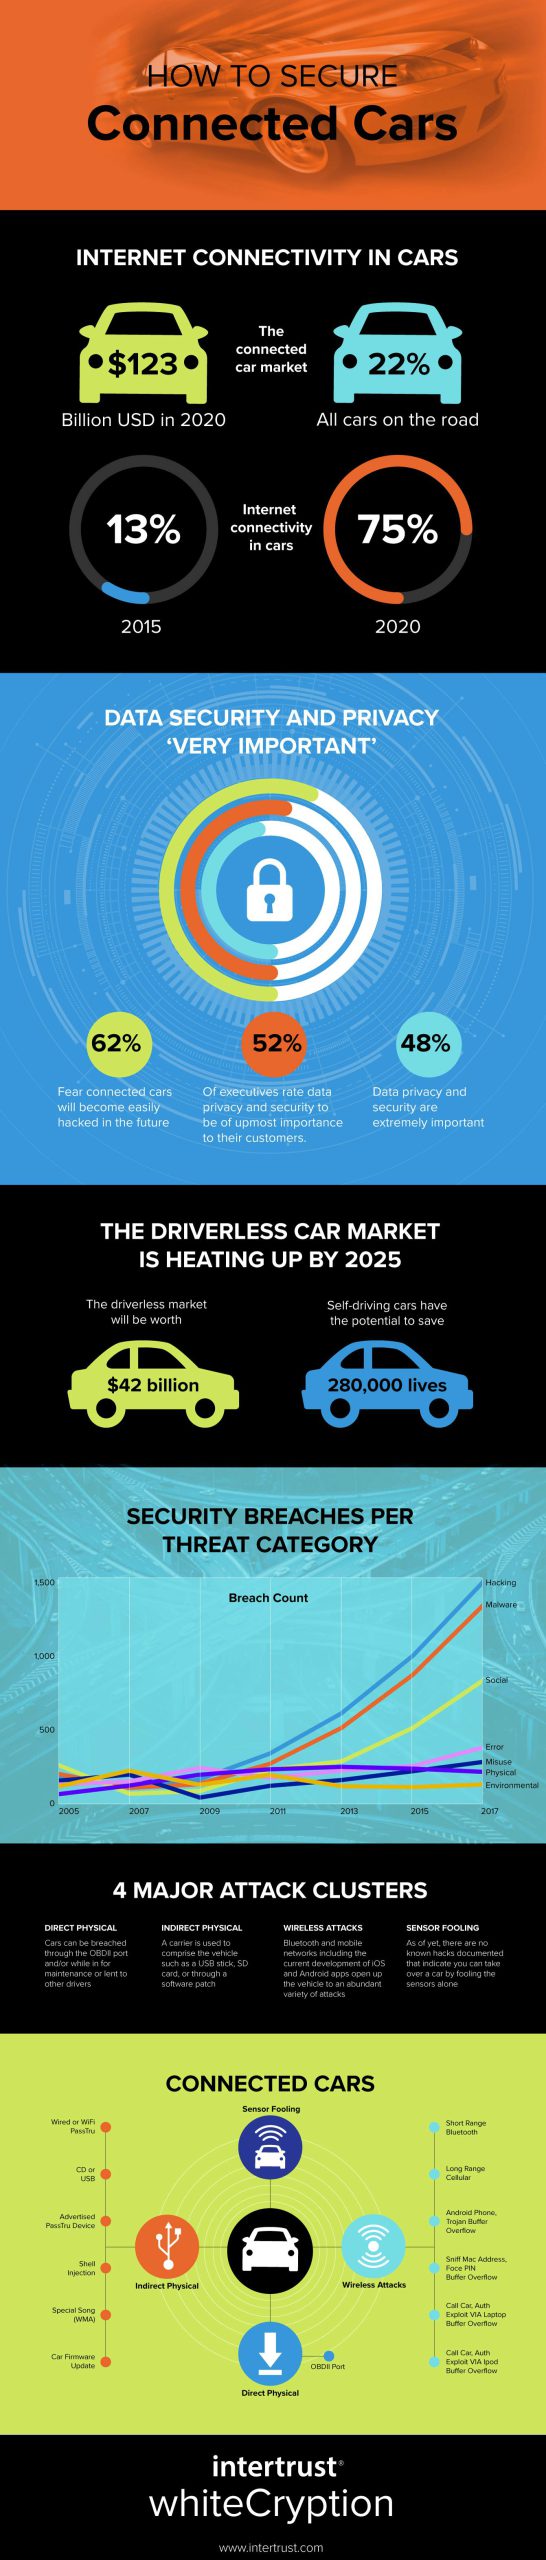

As GM CEO Mary Barra said in a keynote speech, “A cyber incident is a problem for every automaker in the world. It is a matter of public safety.” As Tesla, GM and many others continue to release connected vehicles – and soon driverless vehicles, the dangers are set to increase. In fact, more than half of the vehicles sold today are connected and vulnerable.
By 2025, the driverless market will be worth $42 billion up from nearly nothing with an official market entry still being anticipated [1]. Self-driving cars have the potential to save 292,000 lives annually from preventing collisions. This is in addition to the added benefits of reducing traffic and climate change, along with the costs of car ownership.
While gaining access to, and being able to control or steal a vehicle such as a Tesla is disturbing enough, it raises several concerns about not only connected cars, but also the mobile applications that extend the features of these vehicles. In fact, mobile apps are quickly becoming the main target for malicious behavior. Over the last four years, there has been a 188 percent increase in the number of Android vulnerabilities and a 262 percent increase in the number of iOS vulnerabilities. In addition, according to Gartner, 75 percent of mobile apps would fail basic security tests.
In another report, more than 80 percent of mobile apps on both the Android and iOS platforms revealed cryptographic implementation issues. Recently, Android malware has become more stealth and has begun to obfuscate code to bypass signature-based security software. Despite Google’s response to critical vulnerabilities and patches of critical issues in the Android OS, end users are still dependent on device manufacturers for these updates.