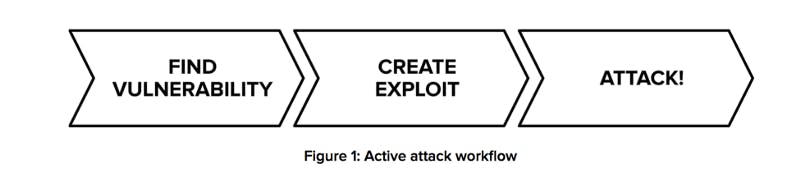
Hackers go about achieving their goals with reverse engineering software to find vulnerabilities they can exploit, data they can extract, or ways to modify the software to do something it was never intended to do. The primary consequences of applications getting hacked include financial loss, destroyed brand reputation, exposure to liability, and regulatory risk.
Over 7 billion identities have been stolen in data breaches over the last eight years equal to one data breach for every person on the planet.
Why do Hackers Attack Mobile Devices and Applications?
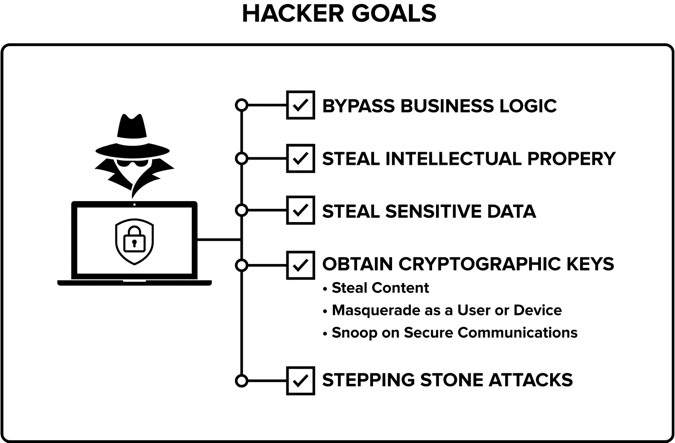
In order to understand threats, we must understand what hackers are trying to achieve. Hackers will mount different kinds of attacks to achieve different kinds of goals. And so, defending against hackers in the context of application security may involve defending against many different kinds of attacks on your mobile device.
Hackers might be interested in bypassing business logic. For example, they might want to bypass controls that let them cheat at a video game or violate the terms of a software license. Of more serious concern is the potential for hackers to bypass controls in safety critical systems. It is not inconceivable that lives could be at risk if a hacker were able to hack a medical device, connected car or some component of critical infrastructure, such as a wind farm, a coal or nuclear power plant, a power grid, or a water treatment facility.
According to a recent study, automobiles today run systems that have more than 100 million lines of code. Those applications often contain valuable intellectual property, which hackers would rather steal than develop. For example, they might be a competitor or a nation state with inferior technology attempting to improve their own products in order to compete more effectively.
Hackers might also be interested in obtaining valuable pieces of data that are managed within the application, such as music or video, financial data, or privacy sensitive health data.
While data can be protected with cryptography, this only shifts the problem from protecting the data directly to protecting the cryptographic keys. Cryptographic keys are not only used to protect data. They can also be used to create a secure identity for a device.
A device may need such a key to authenticate to a cloud service. If a hacker were able to obtain this secret, they might be able to masquerade as that device or as the owner of the device. Cryptographic keys are also used to establish secure communications. For example, HTTPS is a familiar protocol that uses SSL/TLS to secure communication to websites. If a hacker were able to obtain these keys, they could snoop on or alter supposedly secure communications.
For all of these reasons, hackers are highly motivated to steal cryptographic keys embedded in or controlled by an application.